MANAGED SOC · 24×7×365
Detect.Respond.Protect.
A managed SOC that handles incidents, not just alerts on them.
Someone is trying to log in to your VPN for the 400th time.
The question isn't if it will happen.
The question is who will see it, and how fast.
Before we present, we'd like to understand you
Who handles alerts today, and what happens outside working hours?
Which systems are critical to you, and where do the logs come from?
Which regulatory or audit requirements do you need to meet?
What was the last incident that worried you, and how was it handled?
Five minutes of conversation here are worth more than any slide that follows.
The problem isn't the tools. It's what happens between them.
More tools ≠ more protection
Every system adds alerts. Without someone connecting and filtering them, you get more noise, not more protection.
A SOC that forwards alerts forwards responsibility
A service that says "there's an incident" and leaves it to you doesn't solve the problem. It just hands it back to you.
24/7 is math
168 hours a week. Real coverage takes 5–6 analysts on shifts, before tools, training and turnover.
5 questions to ask every SOC provider (including us)
When an incident is detected, do you get an alert, or does someone handle it?
What are you paying for: every data source and every rule, or an outcome?
Is your data in a dedicated, isolated environment, or shared with other customers?
If you leave the provider tomorrow, what stays with you?
How do you reach an analyst at 3 AM: a ticket in a queue, or a direct conversation?
A SOC isn't a product.
It's a commitment to an outcome.
We monitor, detect and respond, and you hear from us only when it really matters.
Some of our clients
What you get, in plain words
Eyes on your organization 24/7/365
A SOC team watching all your systems: nights, weekends and holidays.
Handling, not just alerting
We investigate, block and contain the incident, not just tell you there's a problem.
Updates only when it matters
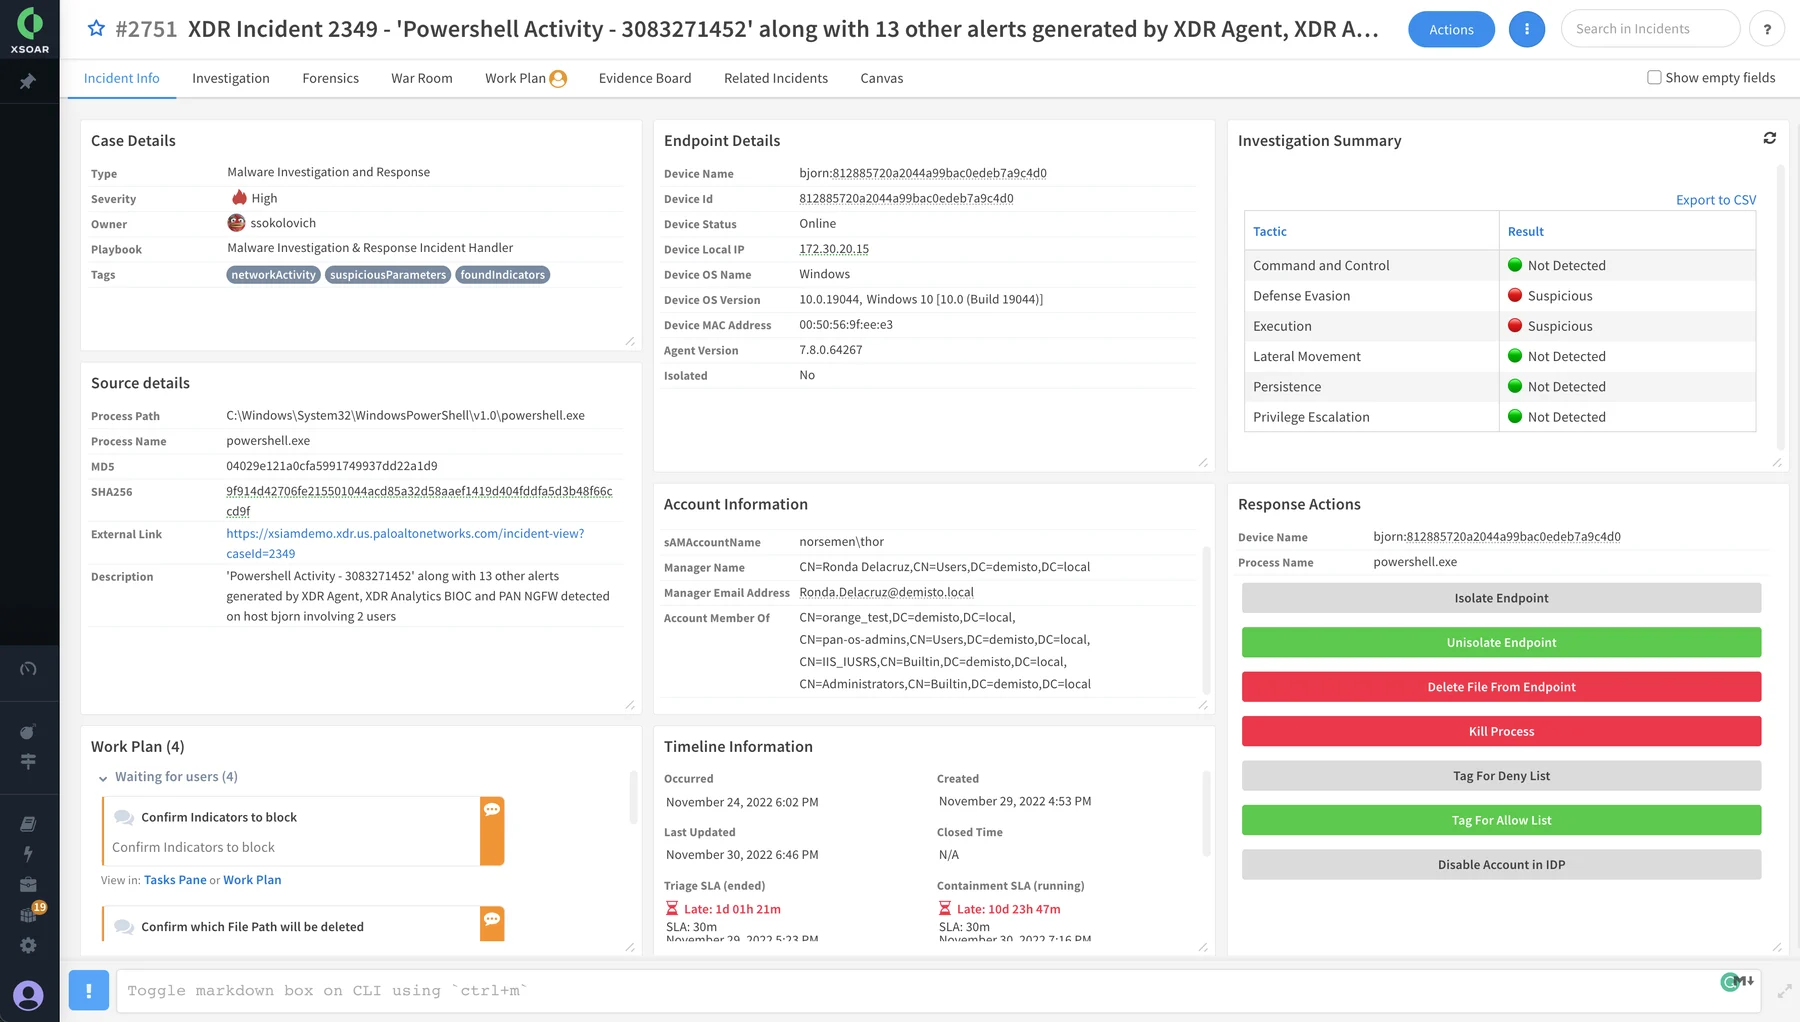
A dedicated Slack channel: what happened, what we did and what we need from you, with one-click actions.
Full transparency
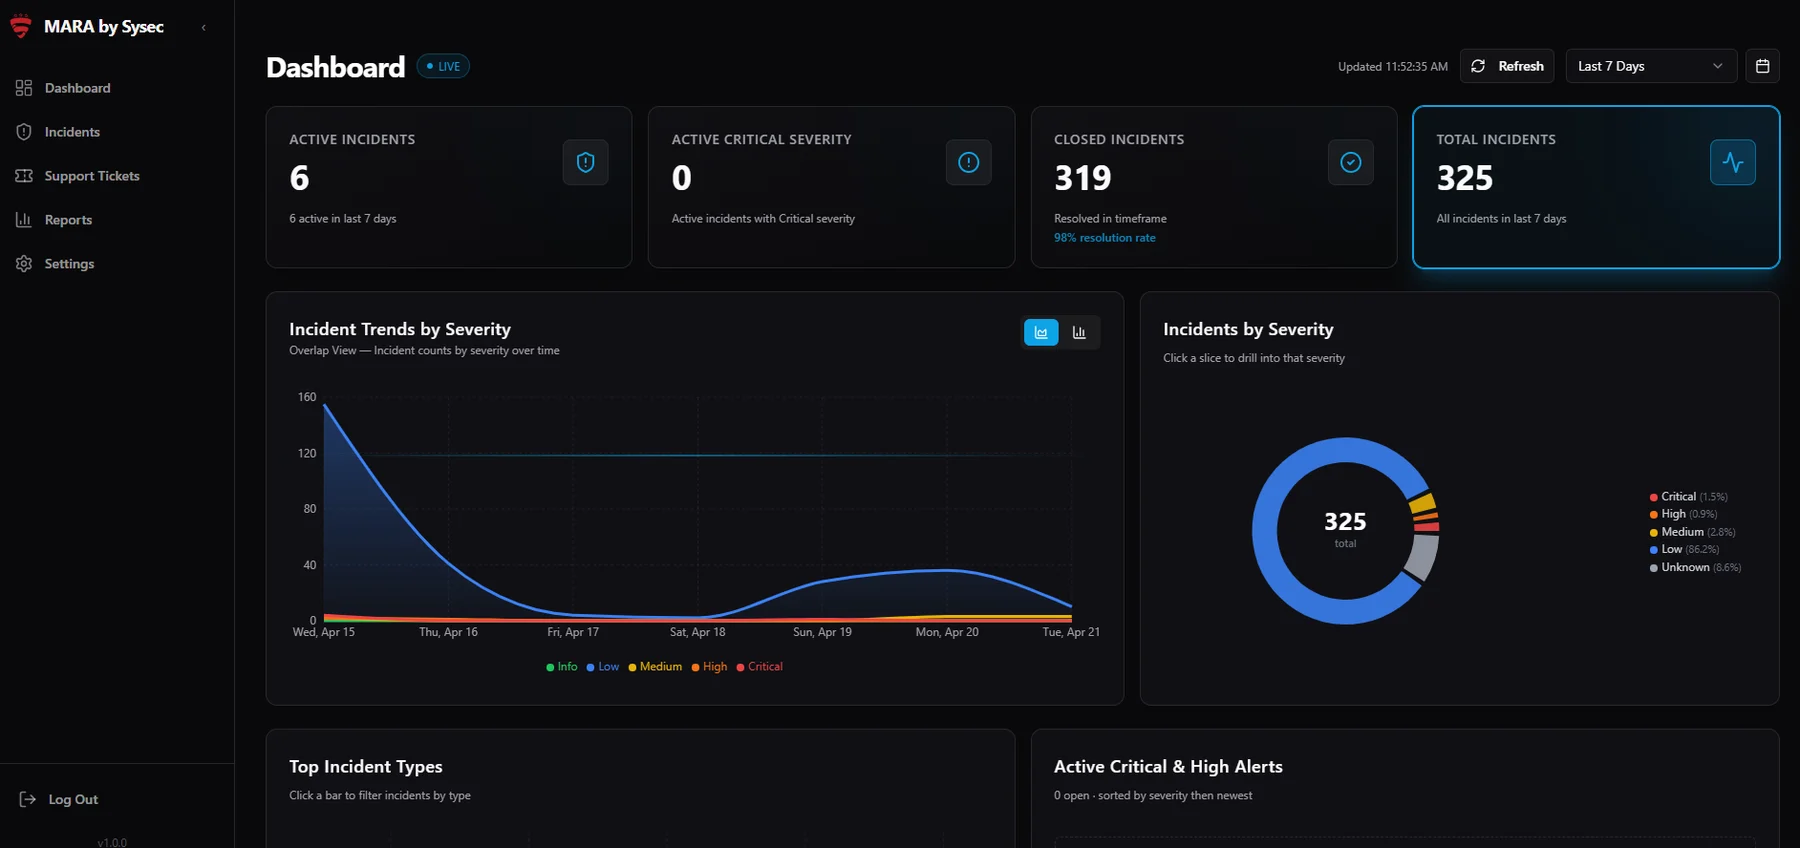
The MARA portal: every incident, action and report, available to you at any moment.
Committed response times
SLA by severity: 10 minutes for a critical incident.
A system that improves, and stays yours
Detection and reports keep getting sharper. If you leave, every setting and all the knowledge stay with you.
And what happens at Sysec at 02:14?
Detection
The SIEM spots a pattern of abnormal login attempts and correlates events from different sources.
Automatic enrichment
An incident opens. AI checks IP reputation, the users involved and history.
First response
A playbook blocks the source address automatically, per a policy agreed with you.
Analyst verifies
An expert analyst reviews, confirms and isolates the endpoint if needed.
You're informed
A Slack message: what happened, what we did, what we need from you.
Morning
A full report in MARA, and the rule is tuned to detect faster next time.
Illustrative scenario · actual response times are set in the SLA by severity
Behind the scenes: how it works
- Collection: all your data sources flow over a secure channel, without replacing any system.
- SIEM: normalization, correlation and analytics. Only real events move on.
- XSOAR: every incident enters a dedicated playbook. Security products also connect directly.
- AI + analyst: AI agents enrich and analyze; a 24/7 SOC analyst decides.
- Outcome: response, containment, updates and reporting, all visible to you in MARA.
CUSTOMER ENVIRONMENT
DATA
COLLECTION
Secure collectorsAgents · APIs
CENTRAL SIEMMulti-platform
XSOARCortex
AI + HUMANINVESTIGATION
RESPONSE &OUTCOMES
SECURITY PRODUCTS direct alerts ↑
We work with the leaders, and with what you already have

Official PS partner of several leading vendors: we deploy, not just monitor.
This is what it looks like in action
Smart automation. Human judgment.
AI & automation
- Check and enrich every alert
- Filter noise and false positives
- Run immediate response actions
Expert analysts
- Verify, investigate and prioritize
- Contain and document the incident
- Reachable directly, no queues
PS expert team
- Deep, complex investigations
- Certified SIEM and XDR experts
- Improve detection over time
What can be automated runs immediately. What needs judgment goes to a person.
Remember the 5 questions? Our answers.
* Subject to technical review and approval · "Common market model" describes things worth checking with any provider
A commitment, not a promise
Active threat / broad impact
Immediate detection and response
Significant threat
Fast, documented handling
Suspected anomalous activity
Investigation and enrichment
Informational alert
Review and documentation
Availability 24/7/365 · response time is measured by incident severity
What it means for everyone around the table
Peace of mind and control
Full visibility, timely response and expert backup in a complex incident.
Predictable cost
No 24/7 hiring, no surprises on the invoice, no vendor lock-in.
Less noise
You get only what needs you, with full context and one-click actions.
Everything documented
Continuous monitoring, full documentation of every incident and regular reports.
Bottom line: you focus on the business; we focus on protecting it.
What happens once we start
Scoping & mapping
We sit together: systems, risks and regulatory requirements.
Connect
We connect the data sources and set up a dedicated environment.
Tailor
Rules, playbooks, and who gets what and when.
Full monitoring
24/7, ongoing reporting and continuous improvement.
Start where it's right for you
Monitoring & detection
- 24/7 monitoring on a dedicated SIEM
- Tailored detection rules
- Alerts and regular reporting
Monitoring & response
- Everything in Essential
- Incident handling and automation
- MARA portal and Slack
Full MDR 24/7
- Everything in Advanced
- Investigation, documentation and containment
- Backup from the PS expert team
Our offer: a posture review with no commitment.
Mapping
Which systems are monitored today, and where the visibility gaps are.
Recommendations
A concrete, prioritized list of what to improve.
Tailored proposal
A track and pricing that fit you: transparent and detailed.
Appendix: 12 things that set our service apart
SIEM as SaaS
Cloud-deployed and fully managed by Sysec: no on-prem infrastructure, with updates and scalability.
A dedicated SIEM per customer
A fully separate, isolated environment: full performance and stronger security.
Proactive handling
Even non-critical alerts are reviewed and improved: less noise, more accurate detection.
Escalation to the PS team
Deep investigations go to certified SIEM and XDR experts.
Continuous system development
Rules, reports and sources are refined throughout the service, not just at onboarding.
Full MDR + investigation
Not just monitoring: investigation, documentation and containment, with analysts available 24/7.
Full data ownership
Settings, rules and the knowledge base stay with you. No vendor lock-in.
Unlimited sources*
Connect as many sources as you like at no extra cost. More connections, more visibility.
Unlimited correlation rules*
Every rule tailored to your environment, with no cap and no extra charge.
Commercial flexibility
From an essential track to full 24/7 MDR, matched to your needs and budget.
Two-way Slack
Alerts, one-click actions (block, isolate, approve) and a live analyst, with no tickets.
Automatic IOC updates
From leading intelligence sources, the Israel National Cyber Directorate and open feeds.
* Pricing is by daily data volume, not the number of systems · rules subject to technical review and approval
01 / 20